
File Identities
File Identities is the fleet-wide index of files UEC has seen.
File Identities is the fleet-wide index of files UEC has seen. It connects an event, inventory observation or scan to the cryptographic identity that policy can use.
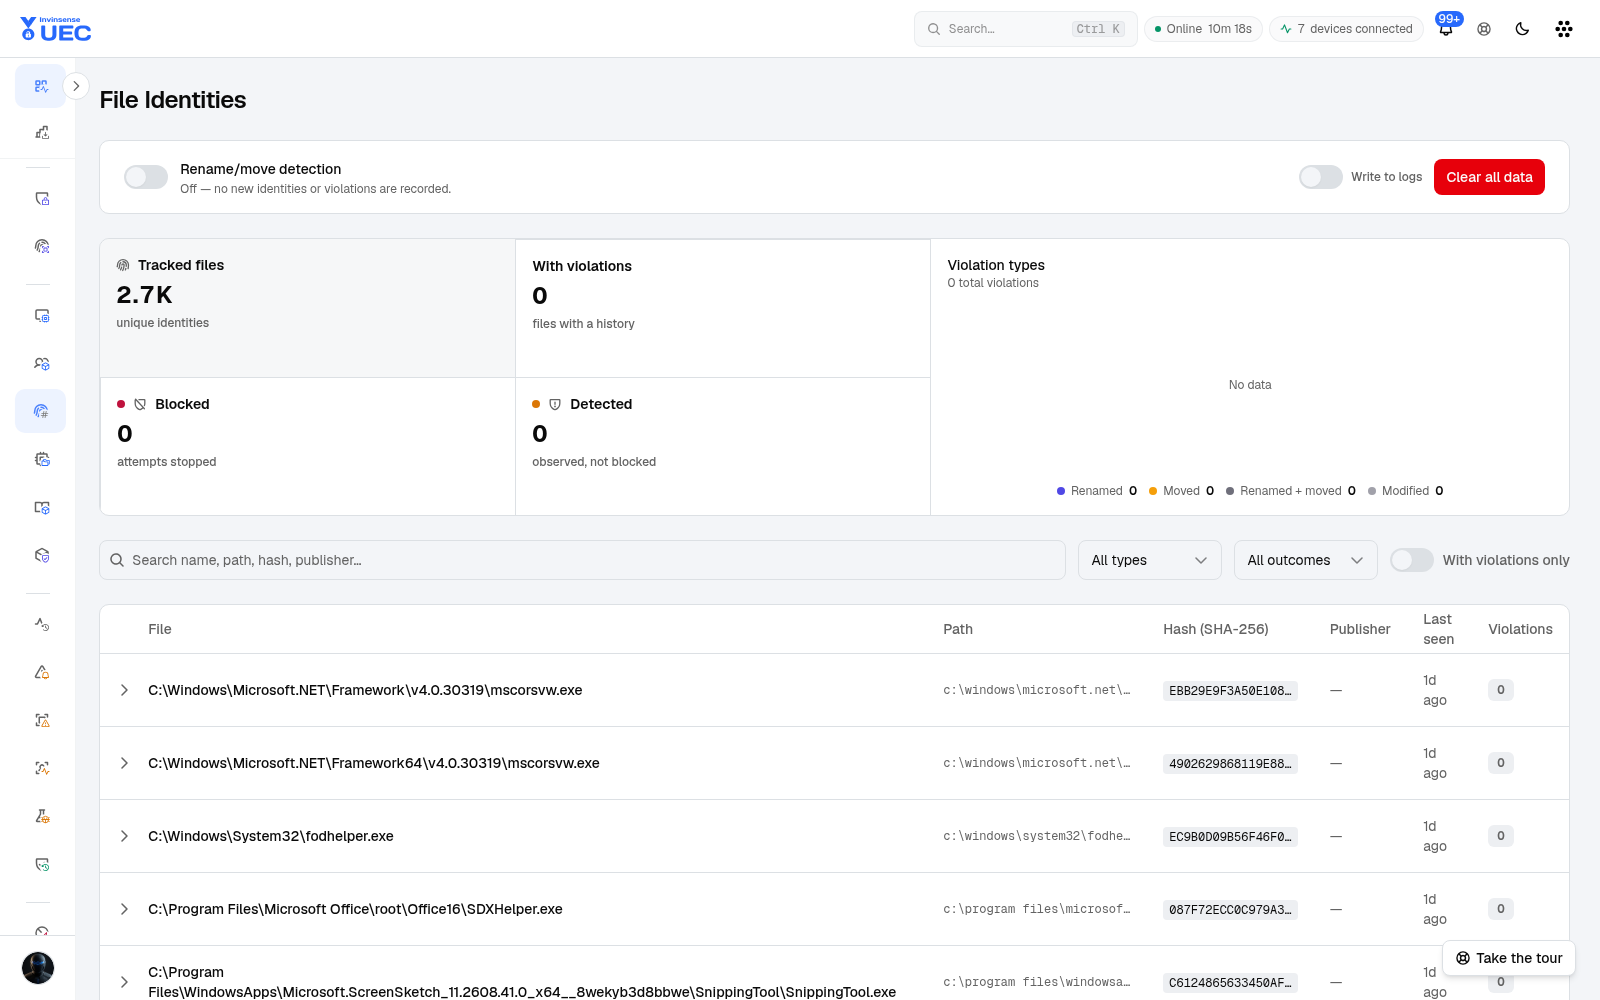
Identity fields
Section titled “Identity fields”| Field | Policy meaning |
|---|---|
| SHA256 / Authenticode hash | Pins one exact binary |
| Publisher / signer | Trusts a cryptographic publisher identity |
| TBS hash | More stable publisher/signer anchor than display text |
| Original/file name | Human context; not a trust anchor by itself |
| Path | Where the file was observed; path-rule candidate |
| Device count | How widespread the identity is |
| First / last seen | Whether it is historical, current or newly appearing |
| Signature status | Valid, unsigned, untrusted chain, expired or invalid |
Common investigations
Section titled “Common investigations”Is this blocked file known good?
Section titled “Is this blocked file known good?”- Search the hash.
- Review signer, publisher and signature validity.
- Check device count and business owner.
- Open recent Events for the same identity.
- If trustworthy, add signer/publisher trust to the smallest useful supplemental group.
- If this is a one-off utility, consider a hash rule.
Is unknown software spreading?
Section titled “Is unknown software spreading?”- Search by file name or publisher.
- Sort by device count and last seen.
- Compare business groups through devices.
- Pivot to Software Catalog for classification and risk.
- Quarantine or deny only after verifying scope.
Did the same file change?
Section titled “Did the same file change?”A new hash with the same signer and file name often means a vendor update. Prefer updating publisher trust if the publisher is trusted; do not create an ever-growing hash list if a stable signer rule is available.
From identity to rule
Section titled “From identity to rule”| Evidence | Preferred rule |
|---|---|
| Trusted publisher, many maintained applications | Publisher/signer |
| One internal binary with stable content | Hash |
| Tool must live in a controlled directory | Path, with path-rule protection considered |
| Malicious family | Deny hash/signer through the appropriate deny workflow |
| Unknown but widespread | Investigate first; prevalence is not proof of trust |
Relationship to other pages
Section titled “Relationship to other pages”- Events proves execution or block context.
- Discovery Scans turns selected observations into candidate rules.
- Software Catalog normalises applications and publishers for humans.
- Policies consumes typed rules.
- Policy Diagnostics computes hashes and inspects signing level for a specific file.