
Identity Exposure
Identity Exposure shows rights that exist on protected hosts: high-privilege hosts, logon accounts and service accounts.
Identity Exposure shows rights that exist on protected hosts: high-privilege hosts, logon accounts and service accounts.
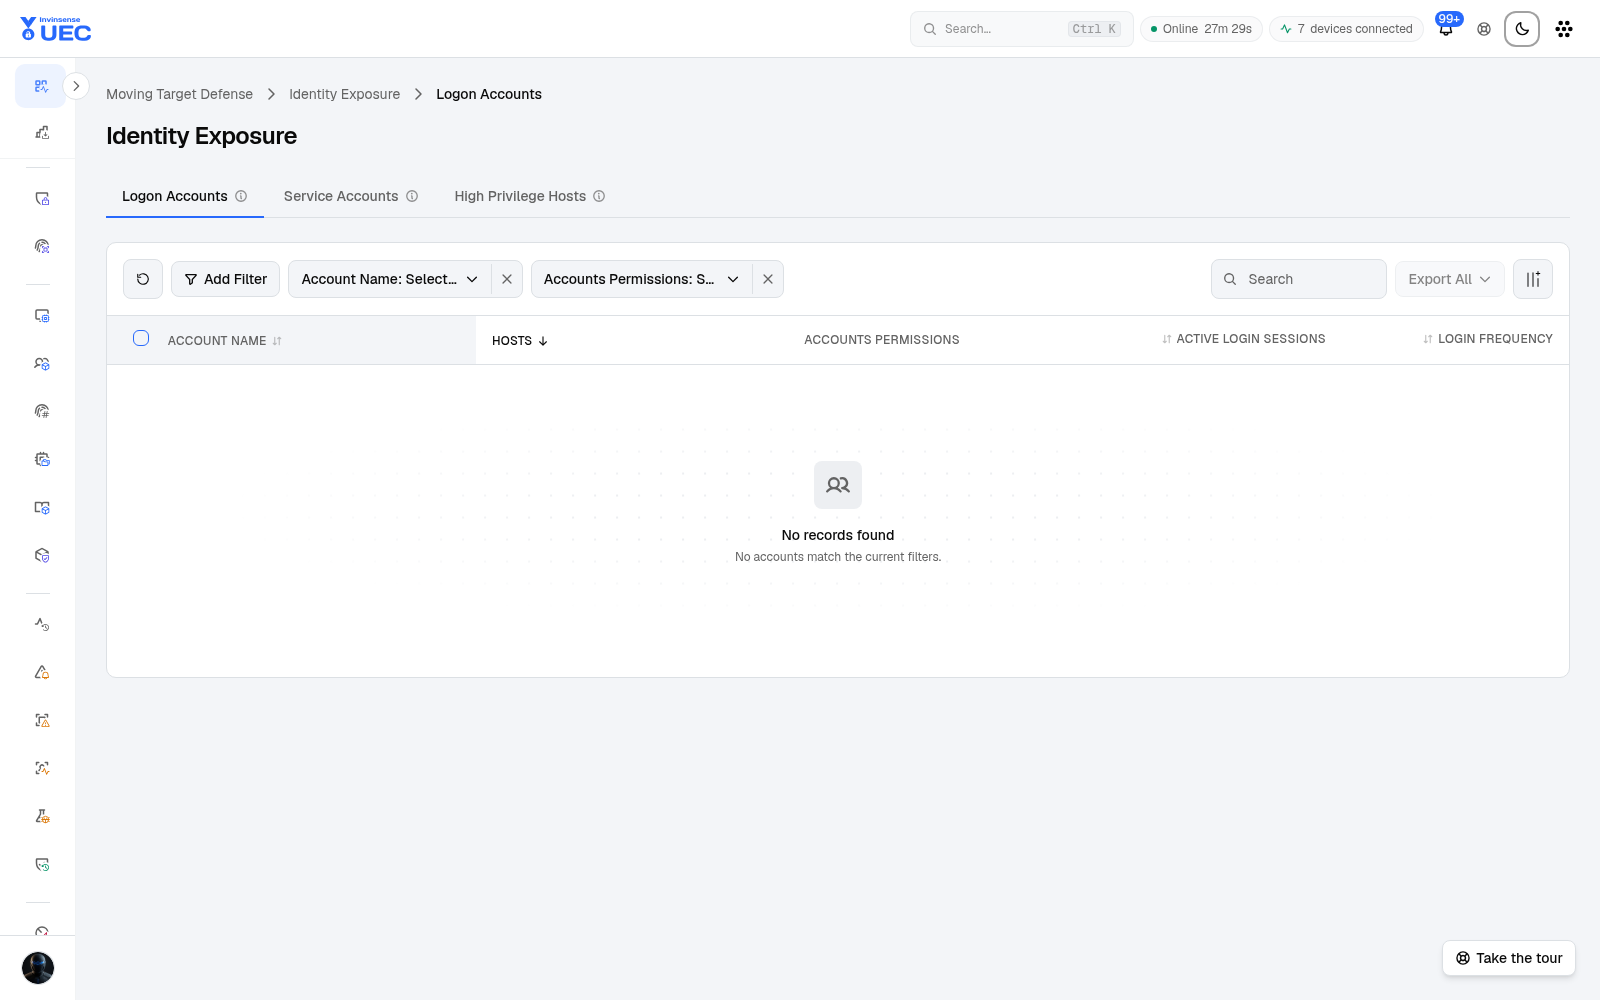
| Tab | Exposure lens |
|---|---|
| High-Privilege Hosts | Machines where privileged rights are concentrated |
| Logon Accounts | Accounts seen logging on and their reach |
| Service Accounts | Non-human identities and host footprint |
Relationship to Behavior Analytics
Section titled “Relationship to Behavior Analytics”AMTD Identity Exposure is a posture snapshot: it shows who has rights. UEC Behavior Analytics is first-party behavior: it scores how identities use access. The two can be read together, but UEBA baselines do not consume AMTD identity data.
Reduction pattern
Section titled “Reduction pattern”- Find accounts with broad host reach.
- Separate human, admin and service identities.
- Remove stale local rights.
- Move service accounts to scoped credentials where possible.
- Use JIT for time-bounded elevation.
- Monitor anomalous use with Events/UEBA.