
Data Exfiltration
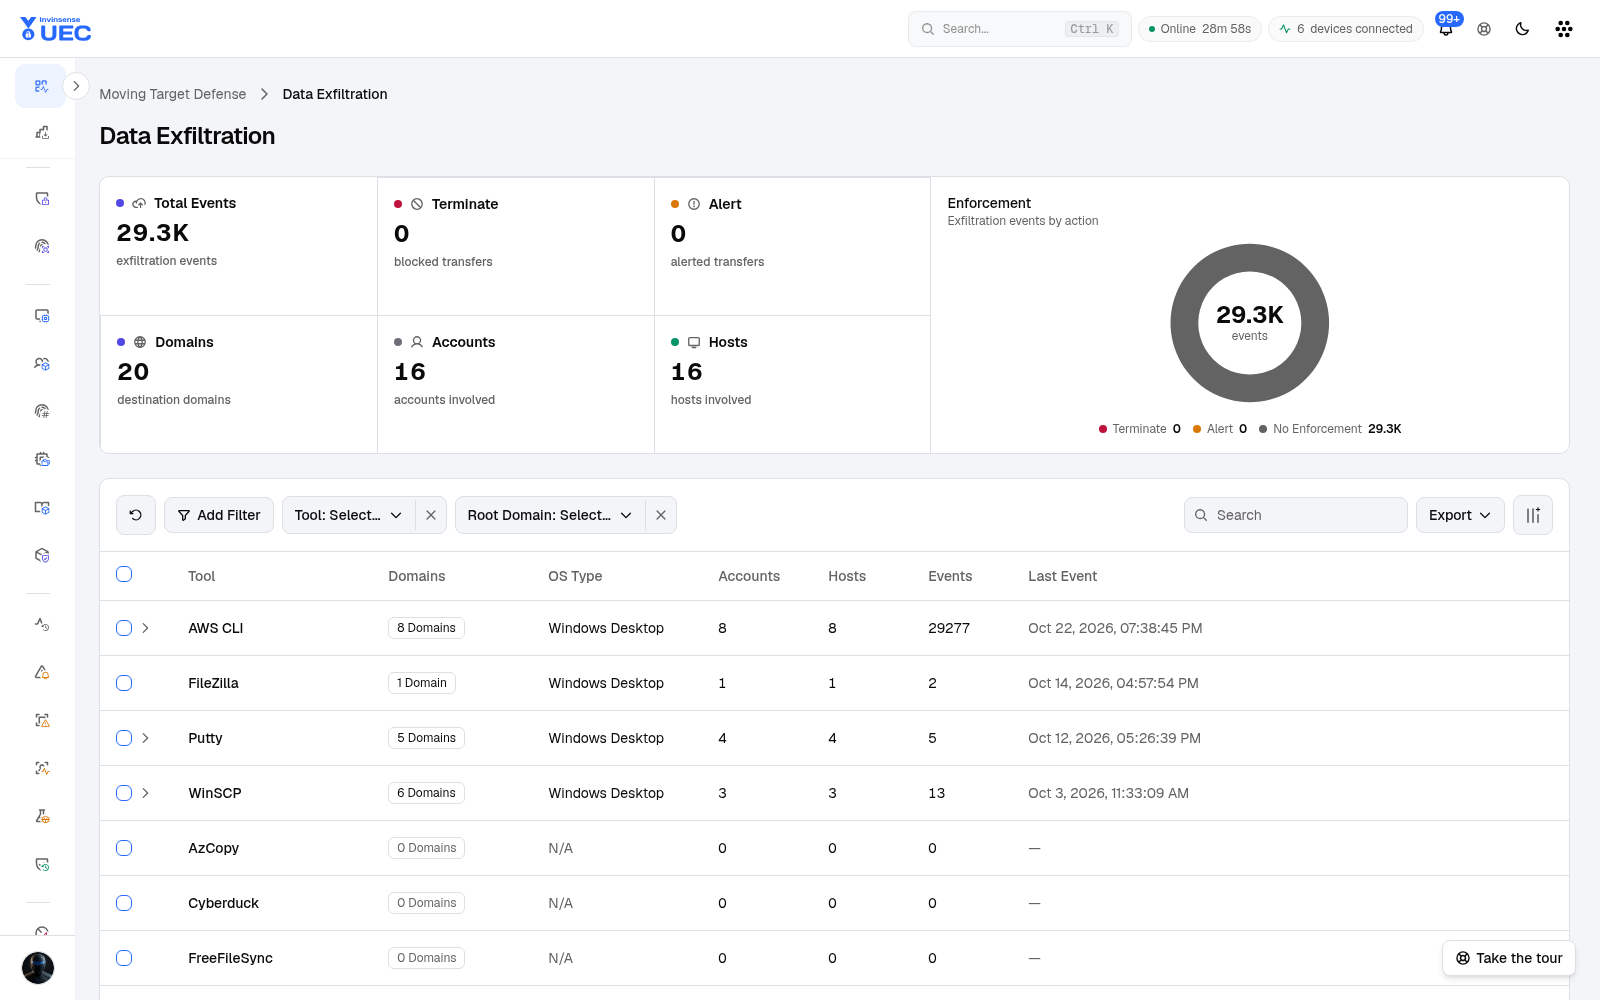
Data Exfiltration reports tools and domains associated with data movement, with enforcement action and event/account/host counts.
Data Exfiltration reports tools and domains associated with data movement, with enforcement action and event/account/host counts.
Overview
Section titled “Overview”The overview shows the last 30 days of exfiltration activity, including event count and an enforcement donut. Tool and root-domain filters narrow the investigation.
Detail fields
Section titled “Detail fields”| Field | Meaning |
|---|---|
| Events | Observed activity count |
| Domains | Destination root domains |
| Accounts | Accounts involved |
| Hosts | Endpoints involved |
| Enforcement | Blocked, alerted or no enforcement |
| OS type | Platform |
| Last event | Recency |
Exports support CSV and JSON. CSV output protects against spreadsheet formula injection because tool, domain, account and host names are attacker-shapeable endpoint data.
Investigation
Section titled “Investigation”- Filter blocked versus no-enforcement events.
- Sort by events and affected accounts/hosts.
- Open tool/domain detail.
- Determine whether the destination is sanctioned.
- Correlate account behavior with UEBA and Events.
- If malicious, contain through Active Response or domain policy.
- If sanctioned, document the business owner.