
Host Risk
Host Risk views the same protected estate through risk lenses: vulnerabilities, security configuration, high-risk software, end-of-life software and control gaps.
Host Risk views the same protected estate through risk lenses: vulnerabilities, security configuration, high-risk software, end-of-life software and control gaps.
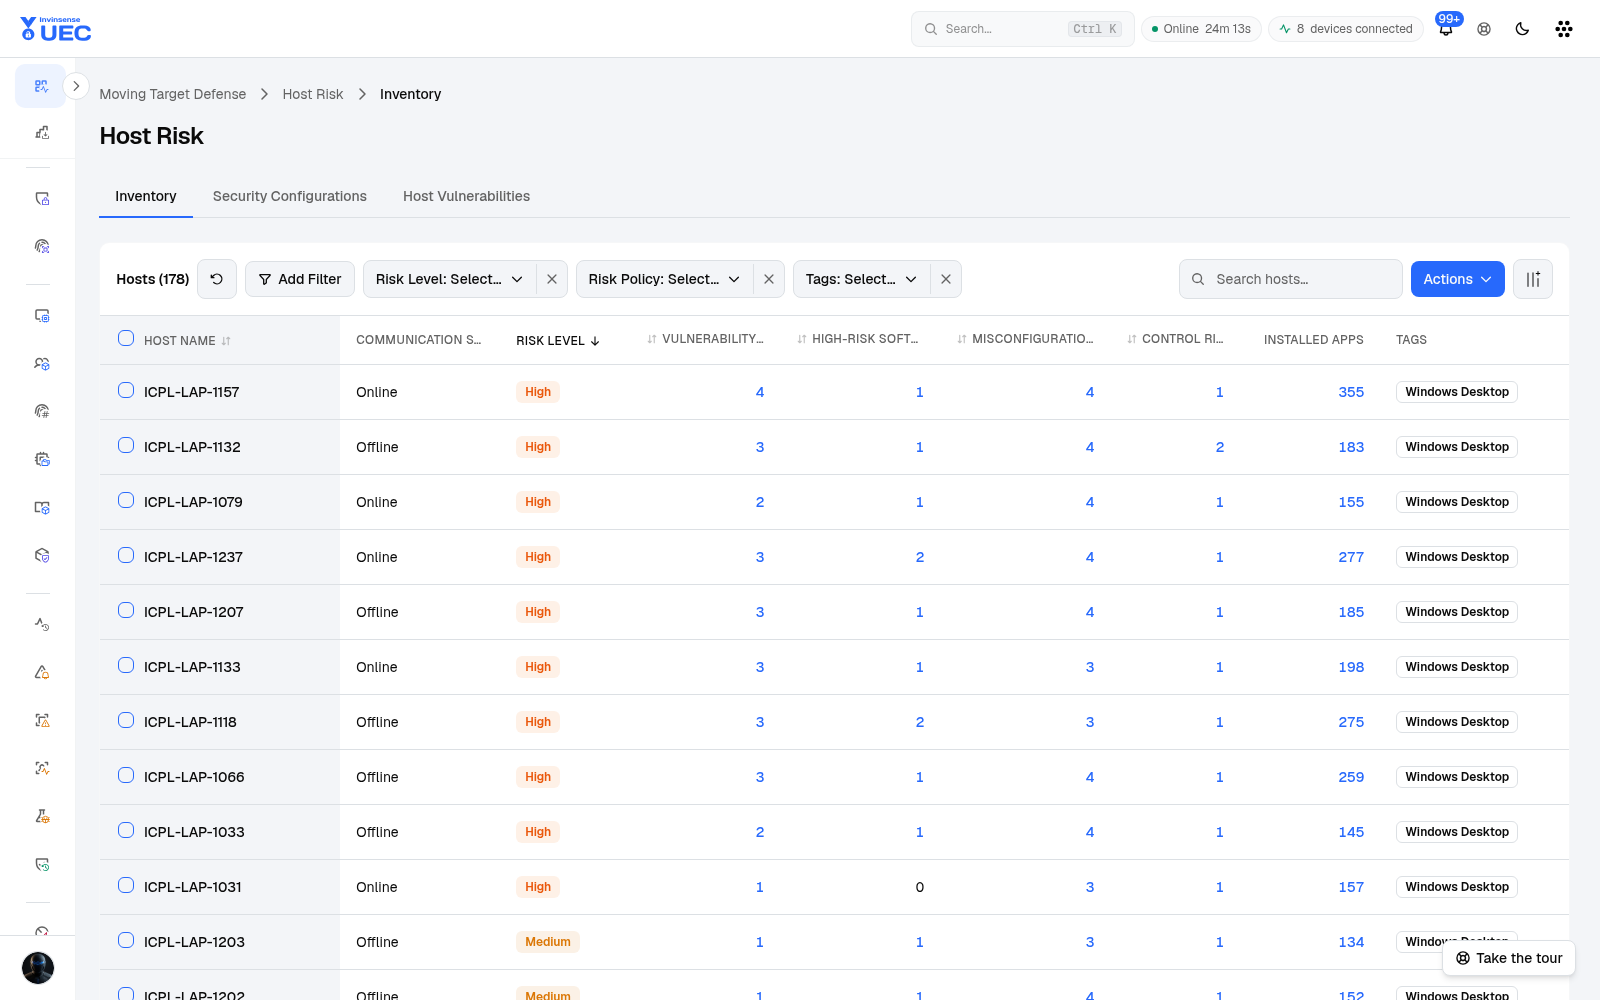
| Tab | Question |
|---|---|
| Inventory | Which hosts exist and what is their total risk/criticality? |
| Host Vulnerabilities | Which hosts carry the most vulnerabilities? |
| Security Configuration | Which hosts have risky configuration findings? |
Host context includes OS type/version, risk level, criticality, group, risk policy, hostname, public/private IP, tags, domain, active user, host ID, MAC, serial number and architecture.
Investigation pattern
Section titled “Investigation pattern”- Start in Inventory and sort/filter by risk level.
- Check criticality tags and business group.
- Open Host Vulnerabilities for CVE context.
- Open Security Configuration for hardening gaps.
- Pivot to the UEC device where response or agent action is required.
- Record risk changes after remediation in Risk History.
A risk level is a prioritisation signal, not a proof of compromise. Pair it with Incidents and Events before responding.