
Certificates
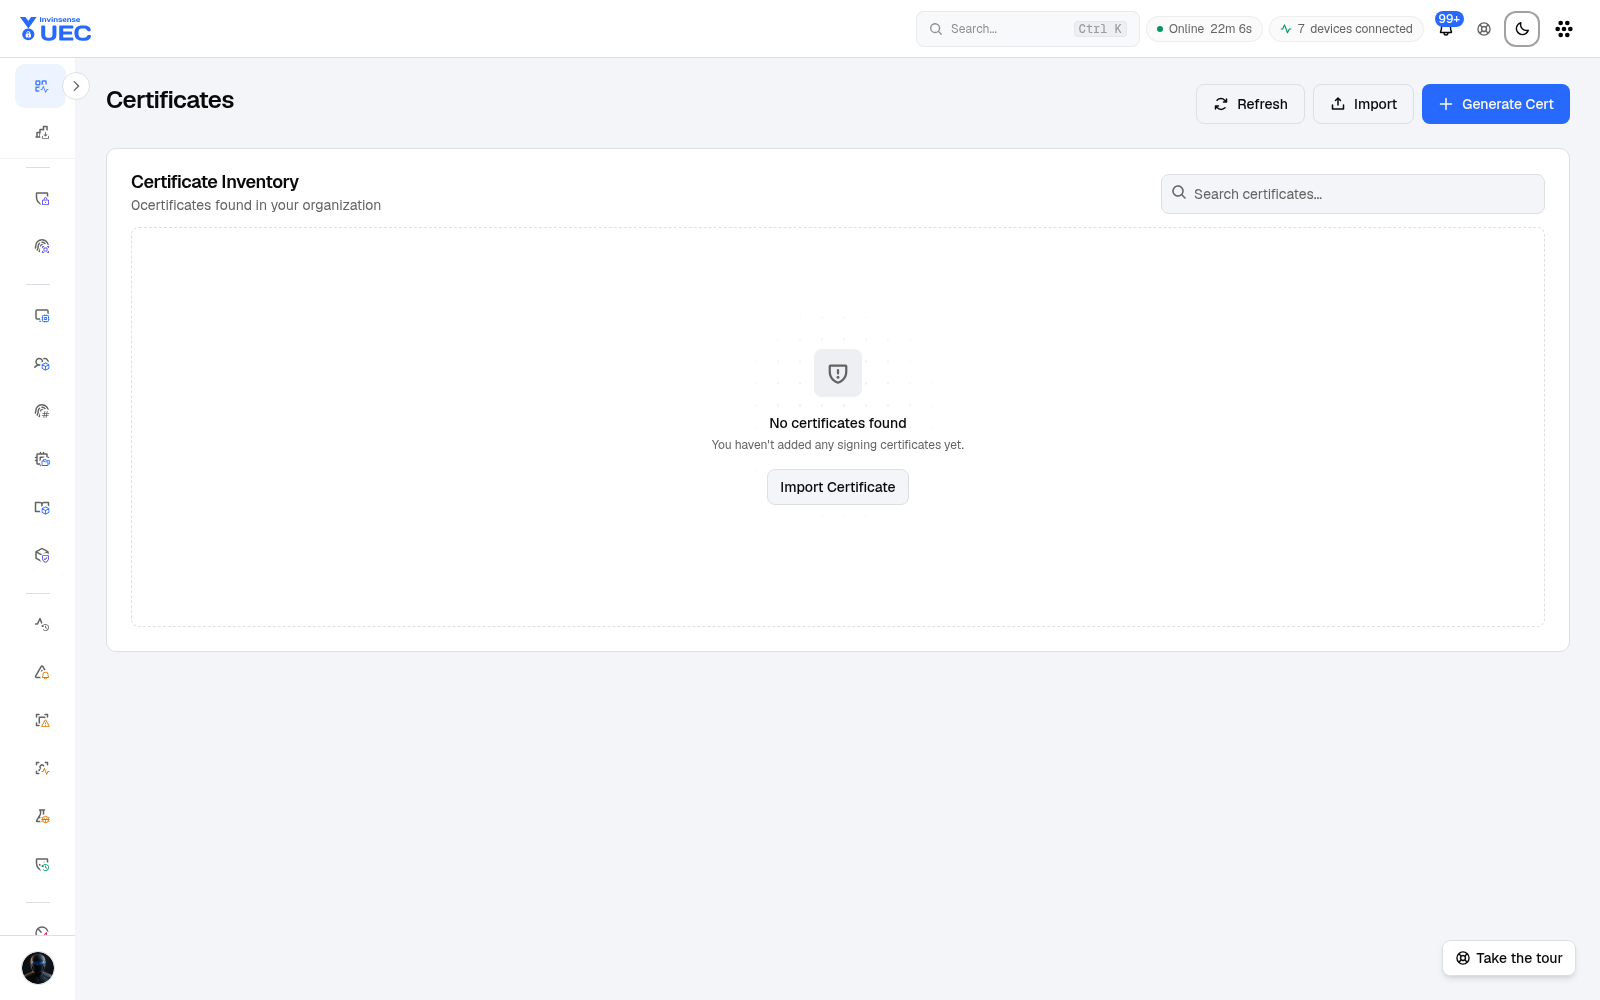
Certificates manages the code-signing and trusted-root certificates that policy trust and endpoint verification rely on.
Certificates manages the code-signing and trusted-root certificates that policy trust and endpoint verification rely on.
Actions
Section titled “Actions”| Action | Use |
|---|---|
| Import | Upload an existing certificate |
| Generate Cert | Create a certificate through the configured signing workflow |
| Search | Find by subject, thumbprint, issuer or friendly name |
| Refresh | Reload the catalog |
Why certificate hygiene matters
Section titled “Why certificate hygiene matters”- Publisher/signer rules are only as trustworthy as the roots and signers you trust.
- An over-broad trusted root can undermine application control.
- Expired certificates can break policy continuation and package validation.
- Duplicate or misnamed certificates make review difficult.
- Private keys must not be uploaded where the product expects public certificate material.
Operational guidance
Section titled “Operational guidance”- Record certificate owner and purpose.
- Set review/expiry reminders before production impact.
- Prefer a narrow signer/publisher rule over trusting a broad root.
- Re-test policy after adding or replacing a certificate.
- Audit every import/generation and assignment.