
Sandbox
The Sandbox integrates ANY.RUN detonation and threat-intelligence lookup while presenting the feature under the product-neutral name Sandbox.
The Sandbox integrates ANY.RUN detonation and threat-intelligence lookup while presenting the feature under the product-neutral name Sandbox. It is module-gated and requires credentials in Settings → Integrations → ANY.RUN.
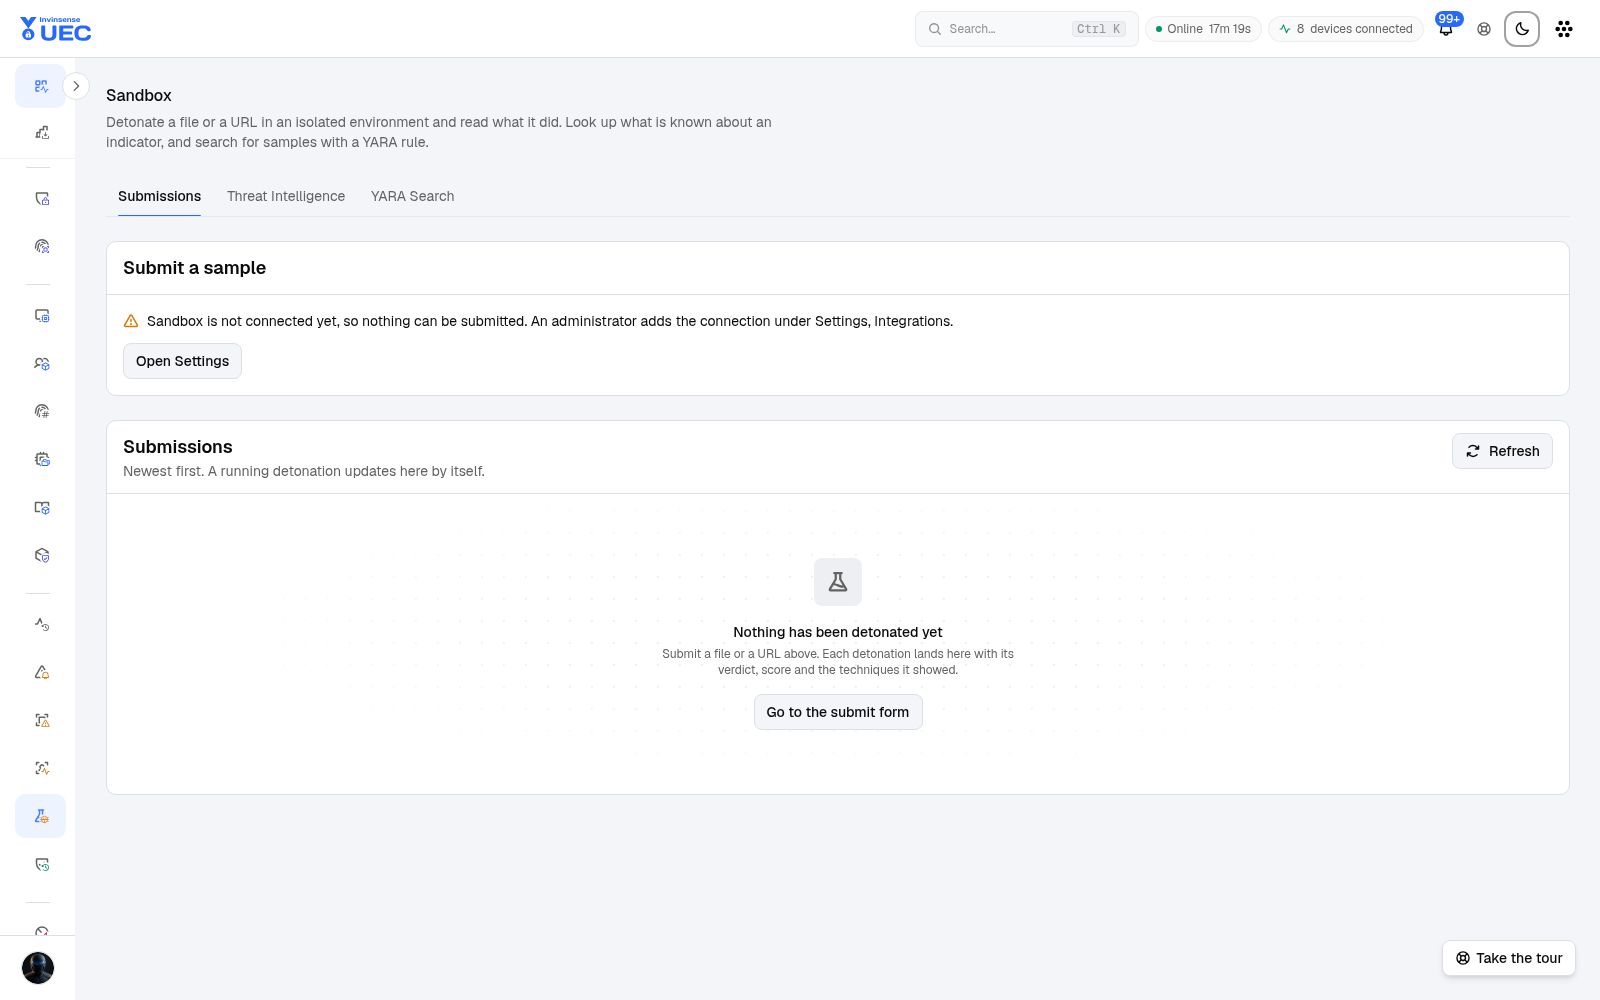
Submit a sample
Section titled “Submit a sample”The submit panel accepts:
- a dragged/dropped file, or
- a URL.
Options include environment OS/bitness, privacy mode, timeout and network toggles. Quota remaining is shown before submit so a request does not fail after the operator has packaged evidence.
Uploaded samples and dropped files are potentially live malware. Downloads are gated behind an explicit confirmation and warning banner.
Submissions and reports
Section titled “Submissions and reports”The list shows status, verdict, score, MITRE tags, submitter and time. A report provides:
| Section | Content |
|---|---|
| Verdict | Provider verdict and score |
| Process graph/tree | Execution lineage |
| Network | DNS, HTTP and connections |
| MITRE ATT&CK | Techniques observed |
| IOCs | Extracted indicators, with promotion into the IOC blocklist |
| Artifacts | PCAP, screenshots, dropped files |
| Exports | JSON, STIX bundle, rendered PDF |
Promoting IOCs sends them into UEC’s reconciled indicator model rather than creating an unmanaged list outside Threat Detection.
Failure behaviour
Section titled “Failure behaviour”| Condition | Behaviour |
|---|---|
| Invalid or refused key | Configuration test surfaces it; submission returns ProblemDetails |
| Quota exhausted | Refused with remaining count before submission |
| Report timeout | Submission fails with provider’s last status, not stuck running |
| Large artifact | Streamed and size-capped; dropped artifacts may be omitted |
| Privacy downgrade | UI states whether a sample will be public/by-link before submit |
Threat intelligence tabs
Section titled “Threat intelligence tabs”- TI Lookup — query an indicator and read provider results.
- YARA Search — run a YARA rule search as an asynchronous job, watch progress and download matches.
These are investigation surfaces; they do not replace endpoint detection pack management.